 Record of Processing Activities
 Transfer Impact Assessment
 Privacy Impact Assessment
 Cybersecurity Controls
 Cybersecurity Risk Management
 Interactive Awareness Program


Asset Inventory Management
powered by osquery
Discover, enroll, and continuously monitor every laptop, server, VPS, and cloud instance your organisation runs. The inventory is collected from the machines themselves — so it is accurate on the day of the audit, not the day it was written.
What is Asset Inventory Management?
The Unicis Asset Inventory Management module turns the endpoints you operate into a live, queryable inventory. It runs on osquery, the open-source agent used to inspect operating systems with SQL, and on Unicis Fleet — our multi-tenant osquery TLS server. You install a lightweight agent, it enrolls with your team secret, and from that moment your inventory maintains itself.
The spreadsheet inventory
- Accurate the week it was written
- Updated when someone remembers
- No idea whether encryption is actually on
- Offboarded laptops linger for years
- Auditor asks "how do you know?" — and you do not
The Unicis inventory
- Reported by the machine, every check-in
- Platform breakdown and totals on the dashboard
- Encryption, firewall, and patch state answered with SQL
- Inactive assets visible and filterable
- Auditor asks "how do you know?" — you show the query and the logs
Enroll Anything You Run
The Add Asset dialog generates the exact install and enrollment command for the platform you pick — already pinned to your team.
From Blind Spot to Evidence
Discovery, live querying, tenant isolation, and framework mapping — in the same platform as your controls and risks.
An Inventory Your Machines Write Themselves
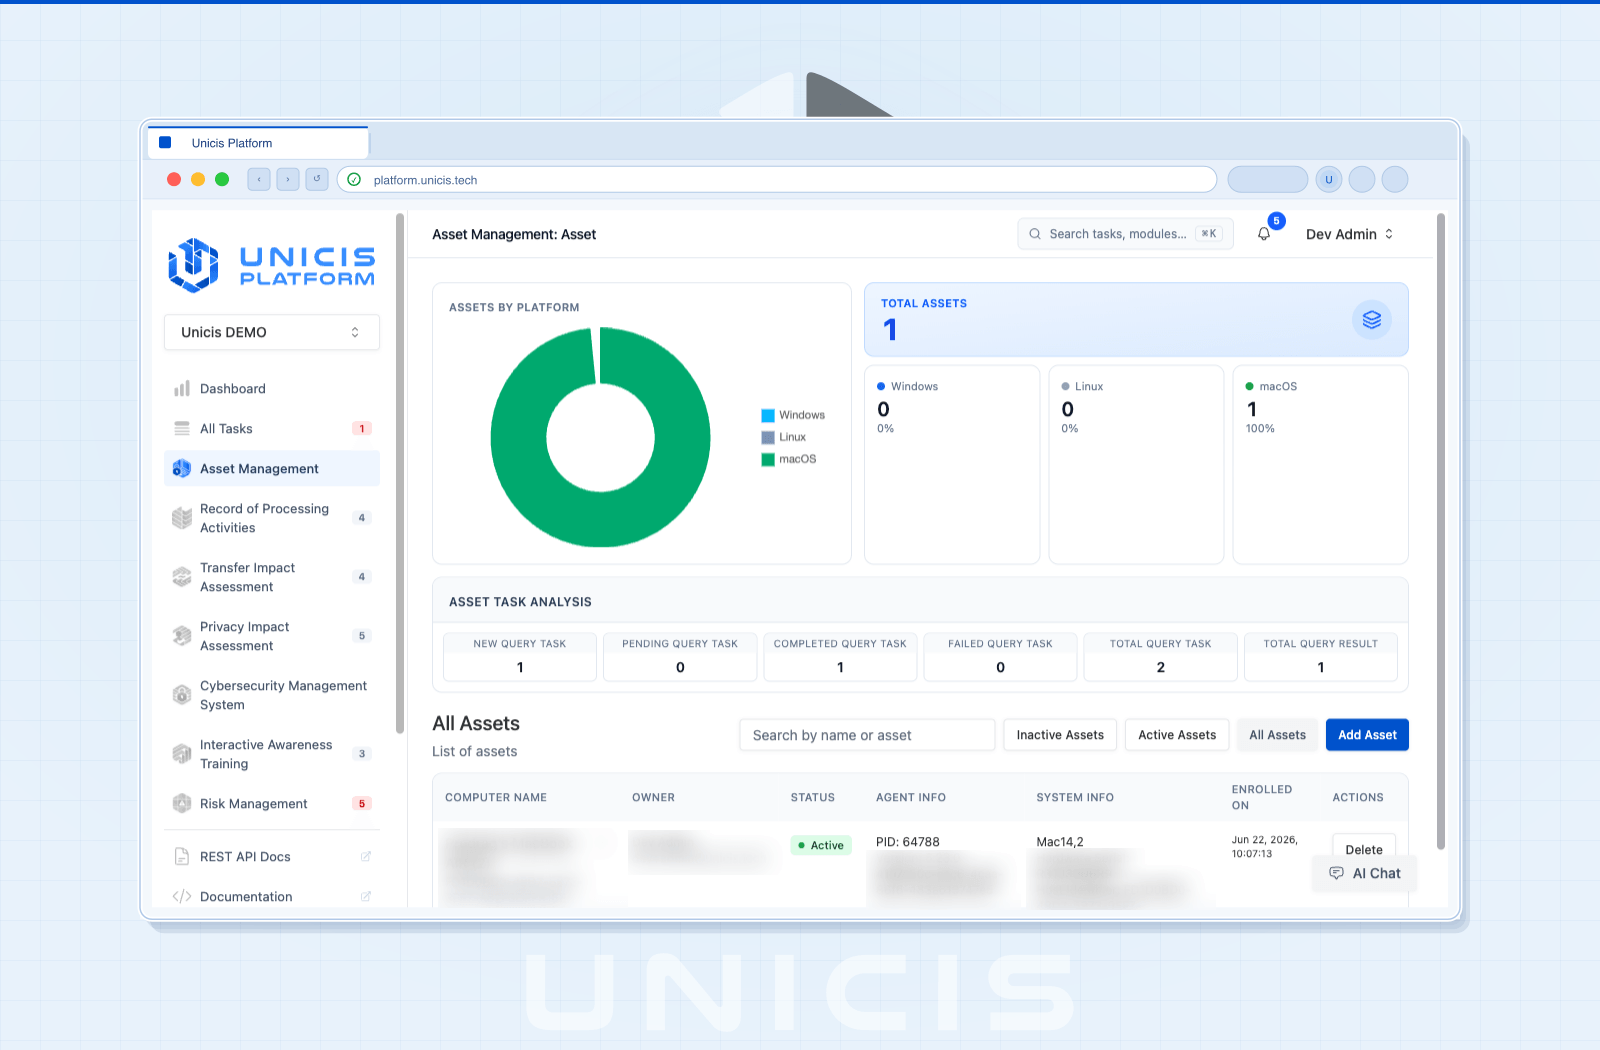
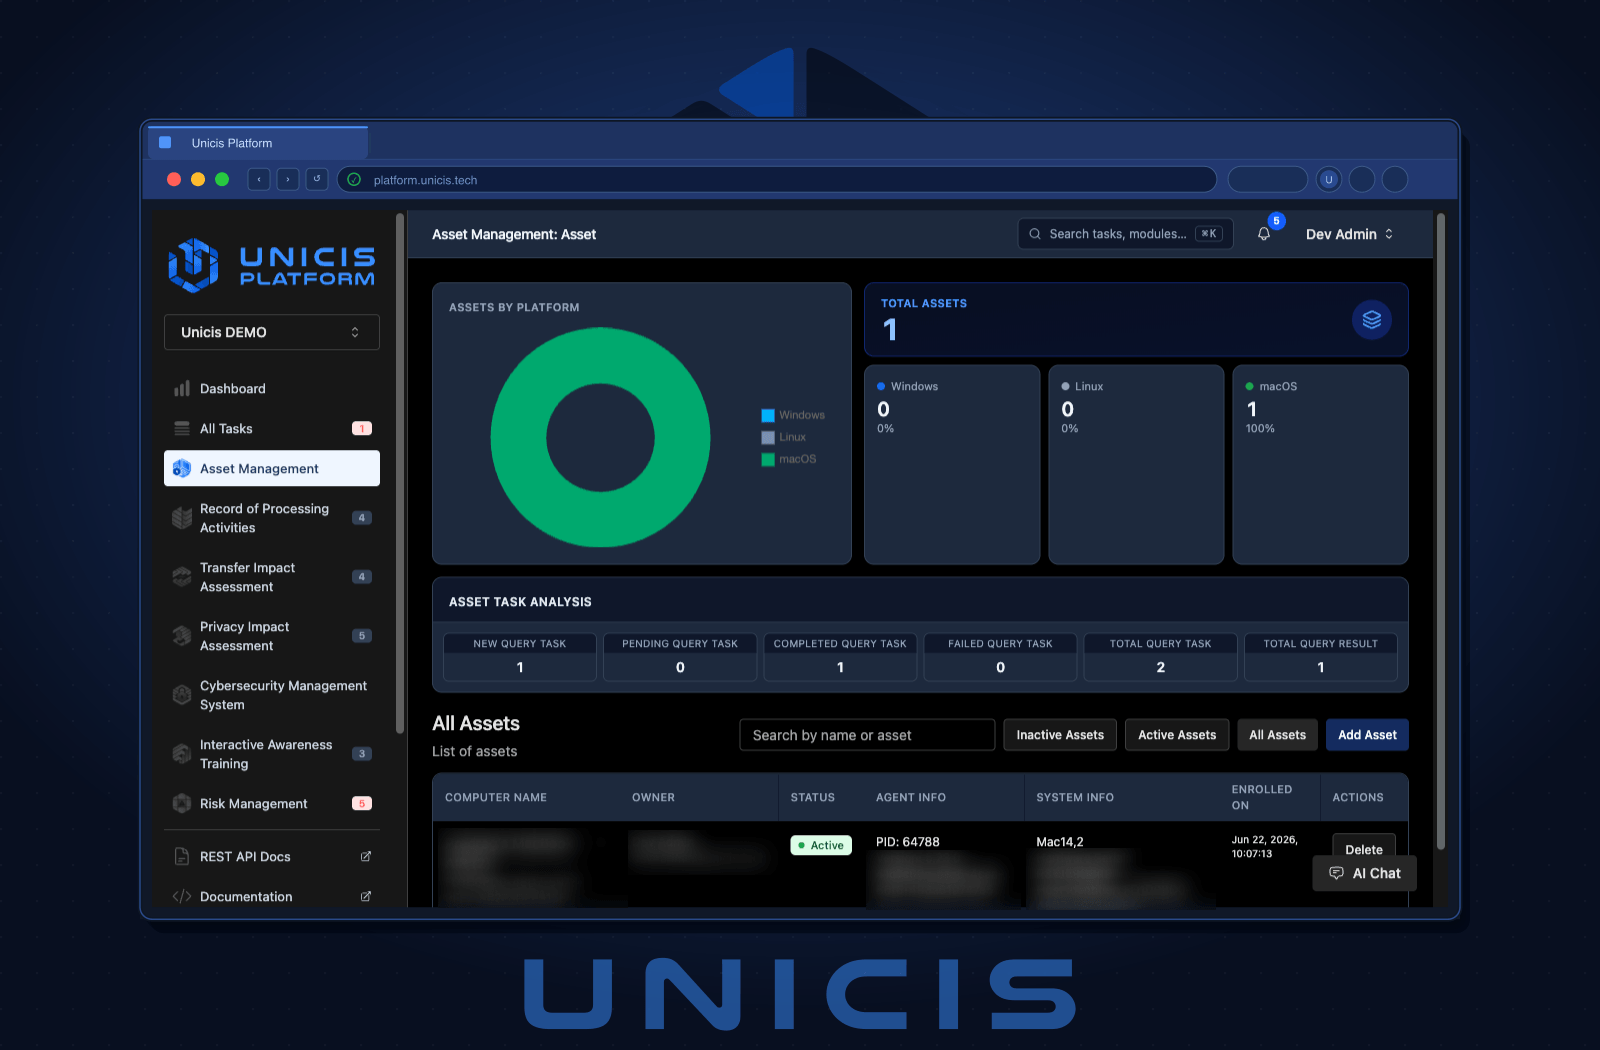
Asset registers go stale the day they are created. Unicis Asset Inventory Management collects the inventory from the endpoints themselves using osquery — the open-source agent that exposes an operating system as a queryable database. Every enrolled machine reports its own identity, platform, and configuration, and keeps reporting.
- osquery agents on Windows, macOS, and Linux (deb and rpm)
- Copy-paste install and enrollment commands generated per platform, pinned to one osquery version
- Advanced tab emits the raw flag set for Ansible, Puppet, Intune, or MDM rollouts
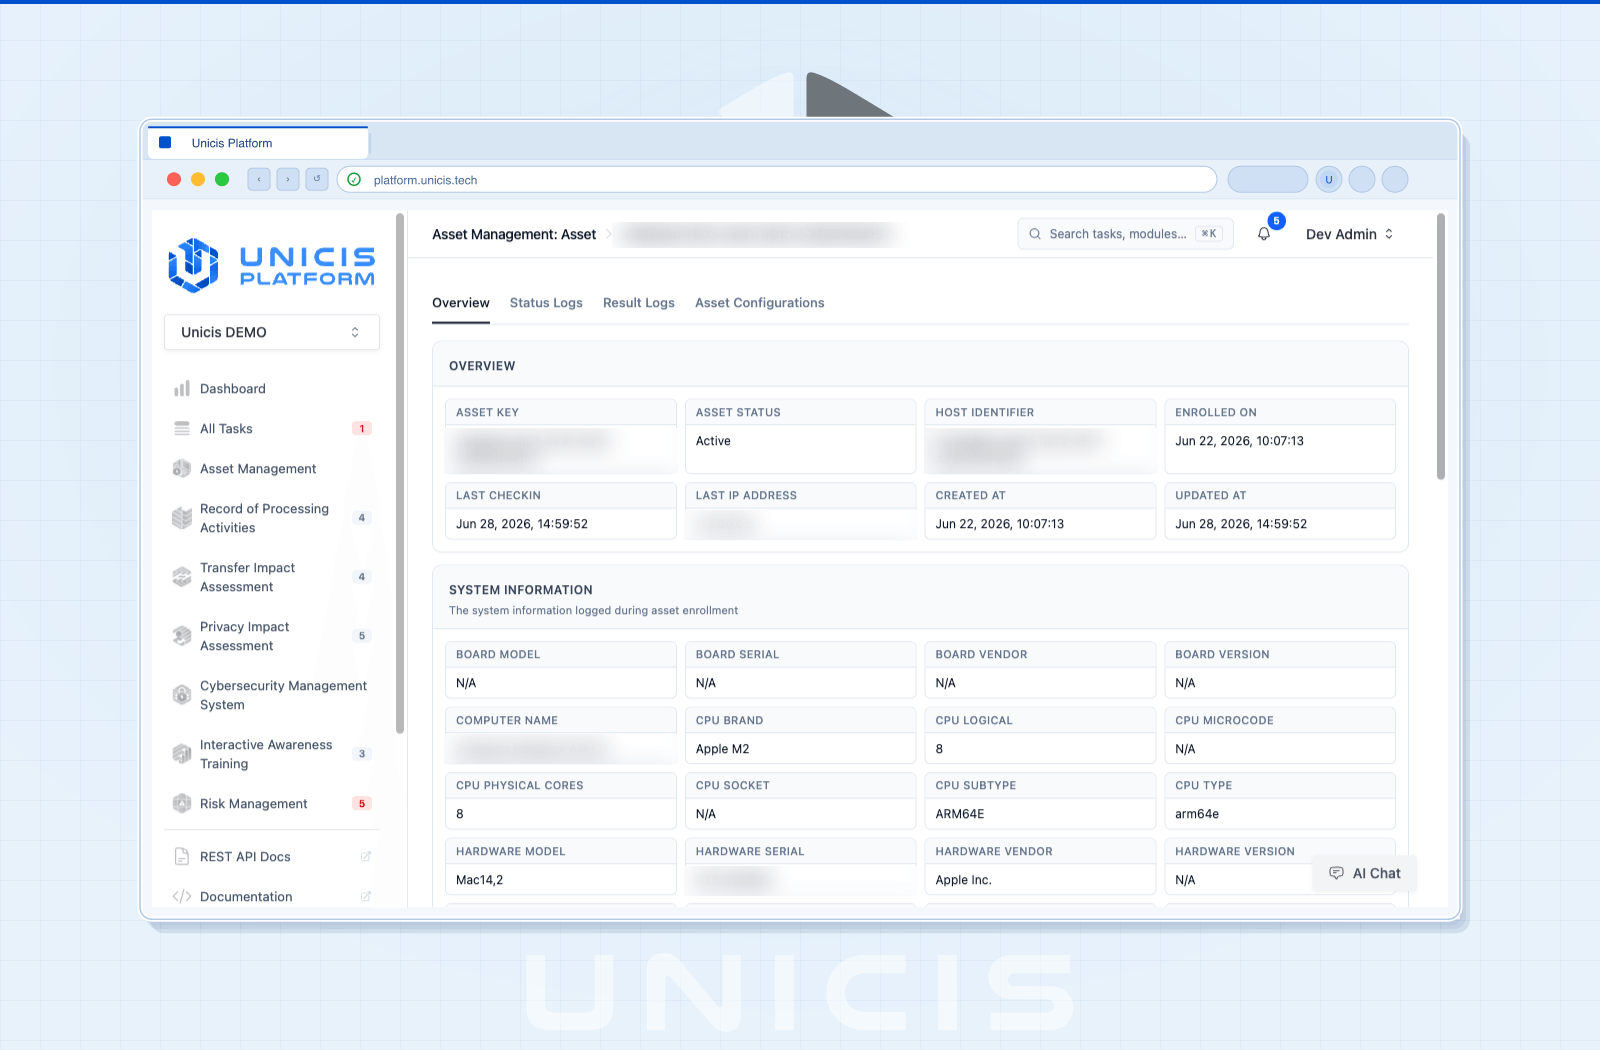
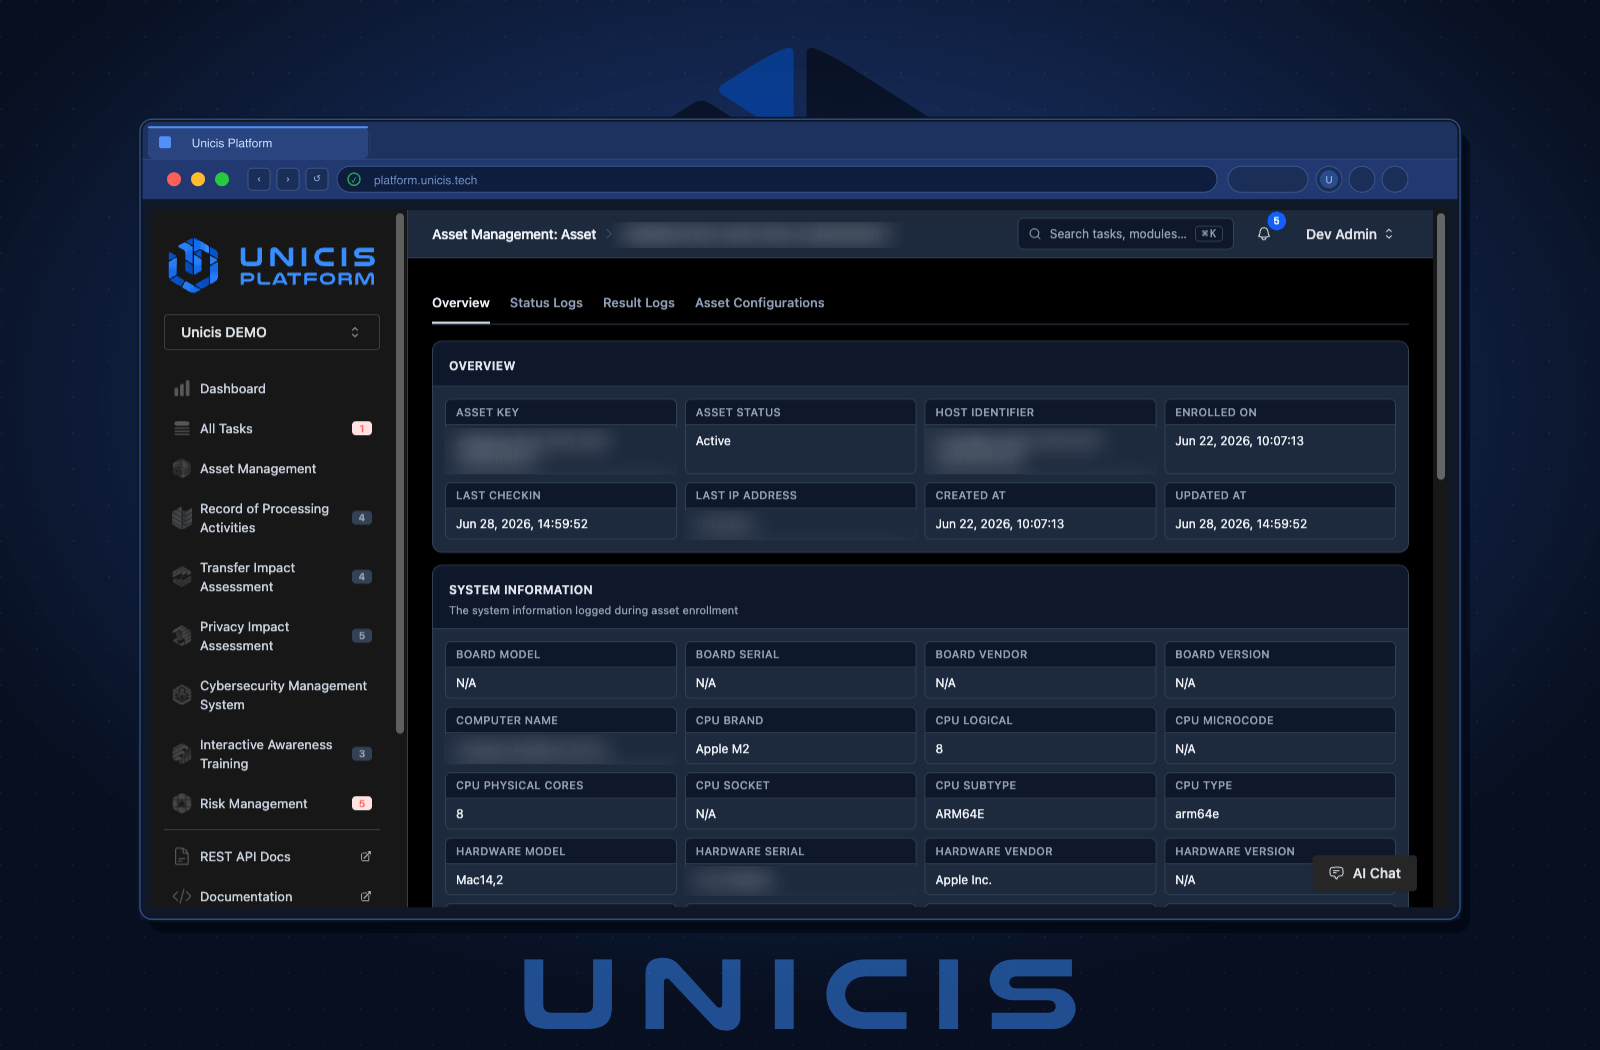
- Assets report platform, enrollment time, and last check-in continuously
- Searchable, filterable, paginated asset table — active and inactive
Ask Your Fleet a Question, Get an Answer
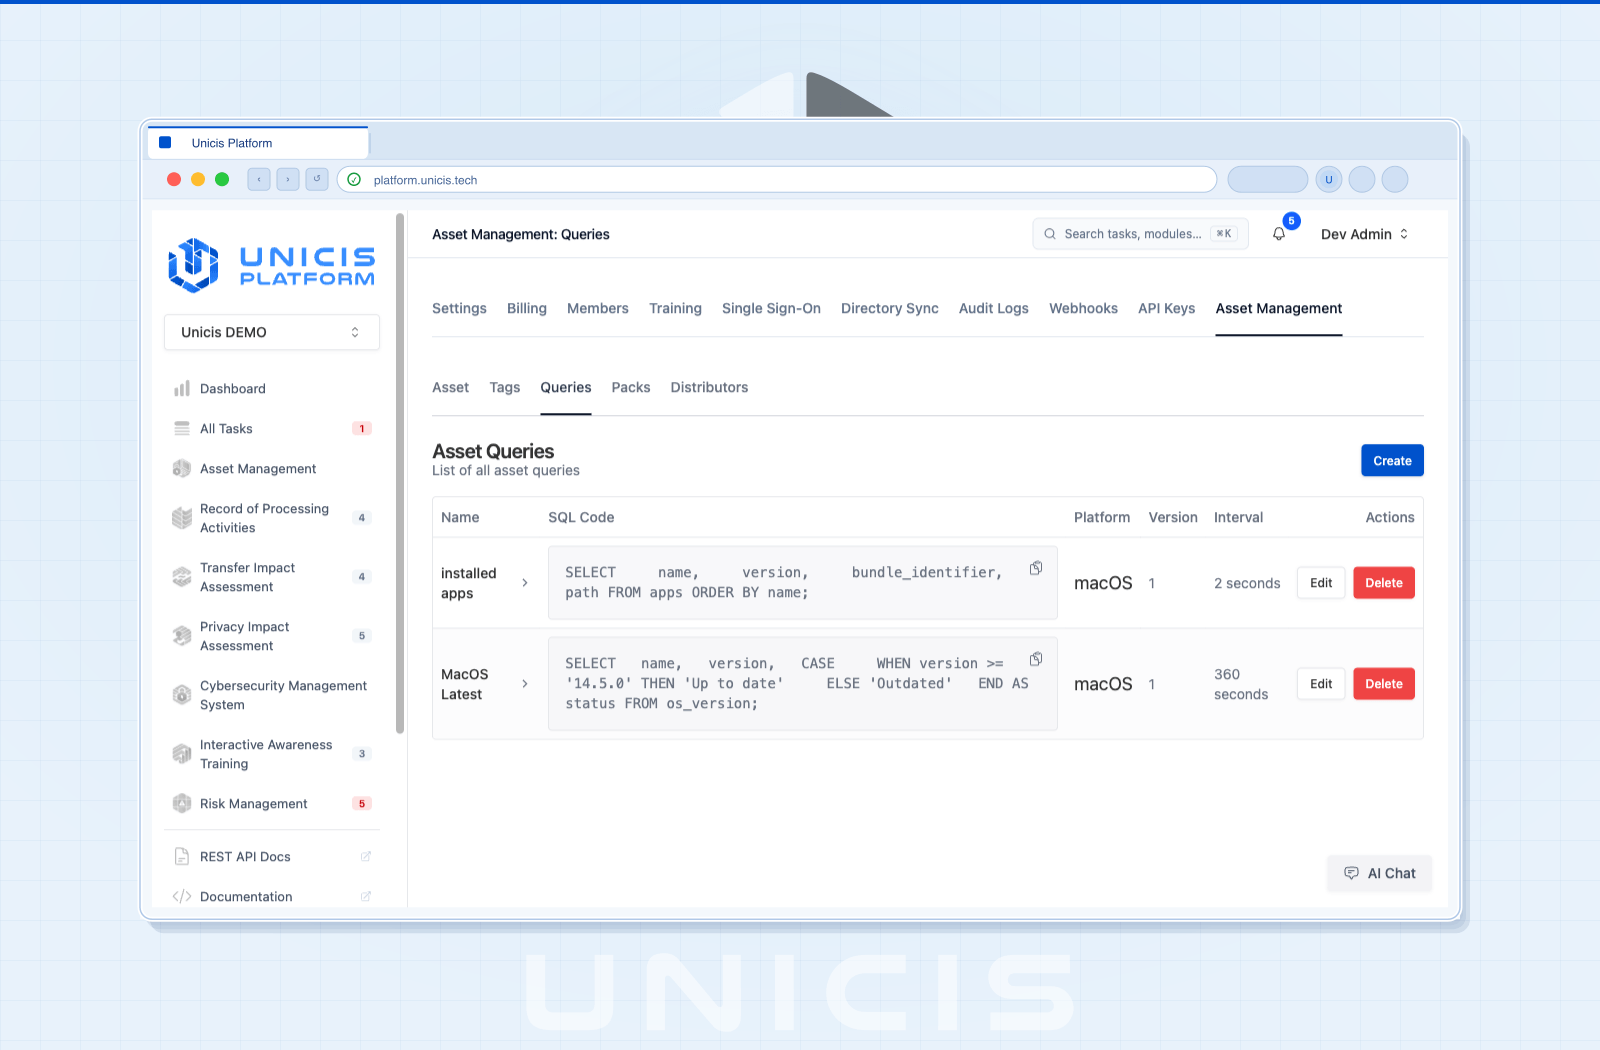
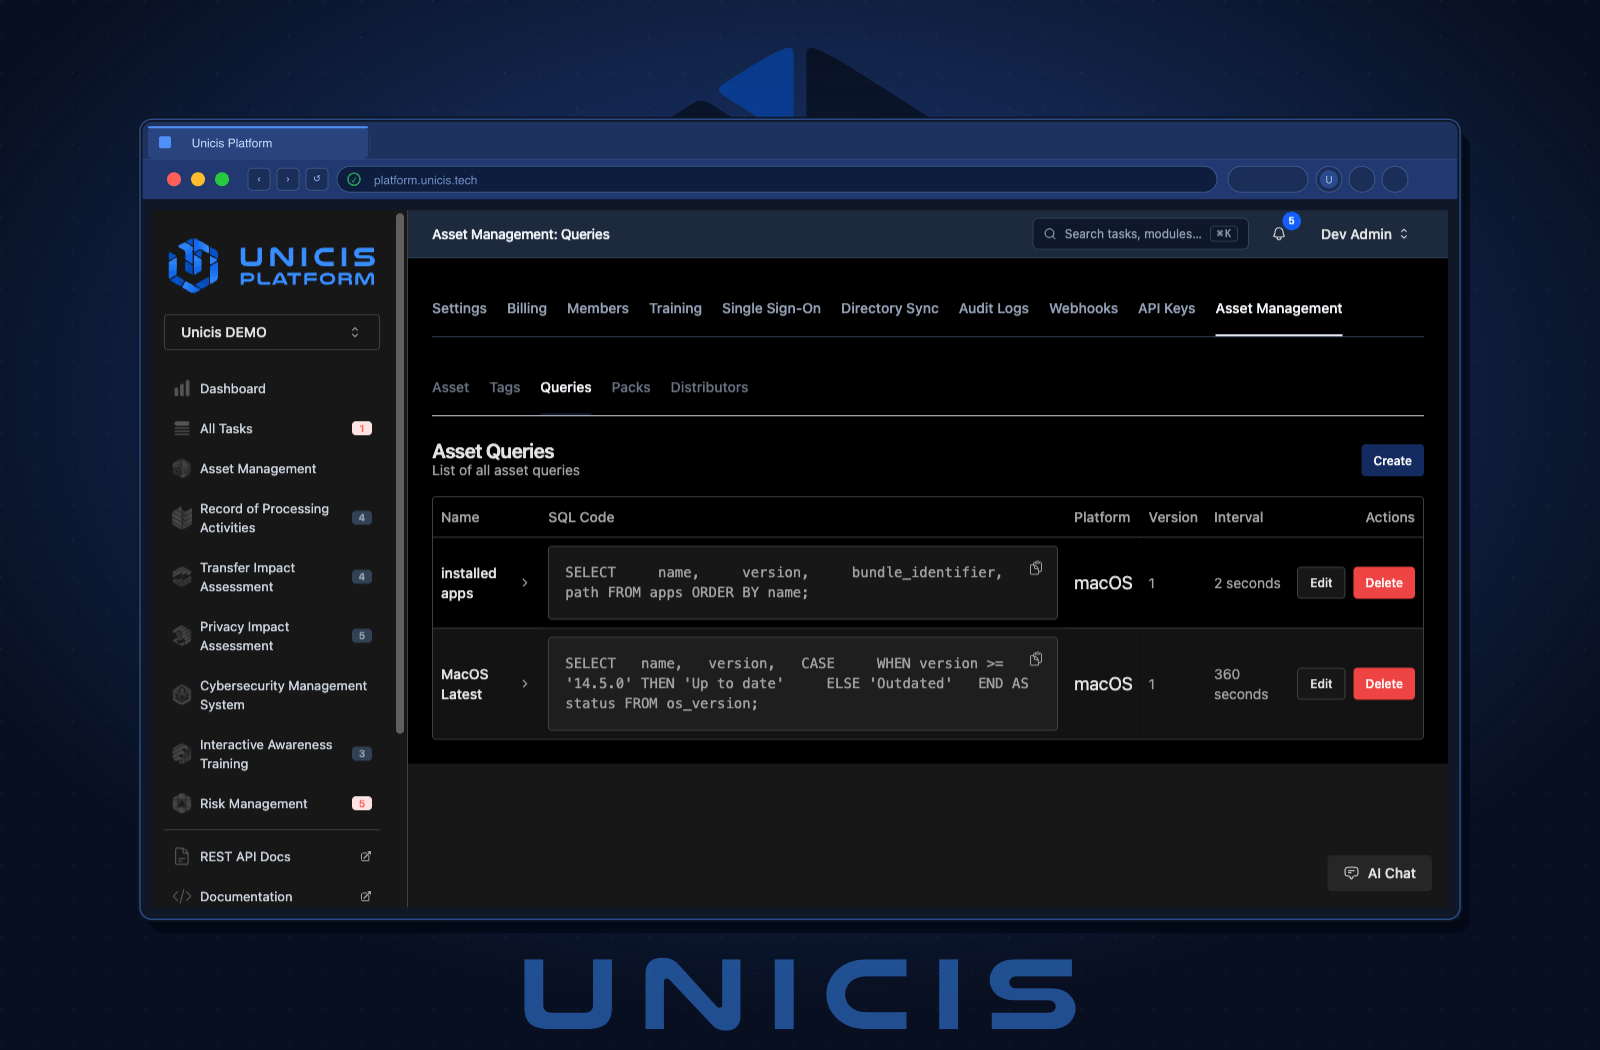
Saved queries turn compliance checks into SQL you write once. Is disk encryption enabled? Is the firewall on? Which machines still run that vulnerable package? Schedule them in packs for continuous monitoring, or fire a distributed query and get answers from live machines during an incident.
- Saved queries with SQL body, platform target, and a schedule interval from 1 hour to 1 month
- SQL validated in the browser — single, read-only SELECT statements only
- Packs group queries on a schedule and attach to tags
- Distributed (live) queries with new → pending → complete / failed result tracking
- Results name the asset, its owner, and the host identifier — failures show the error, not an empty table
- Configuration overview showing exactly what each node received
Tenant Isolation, Not Shared Buckets
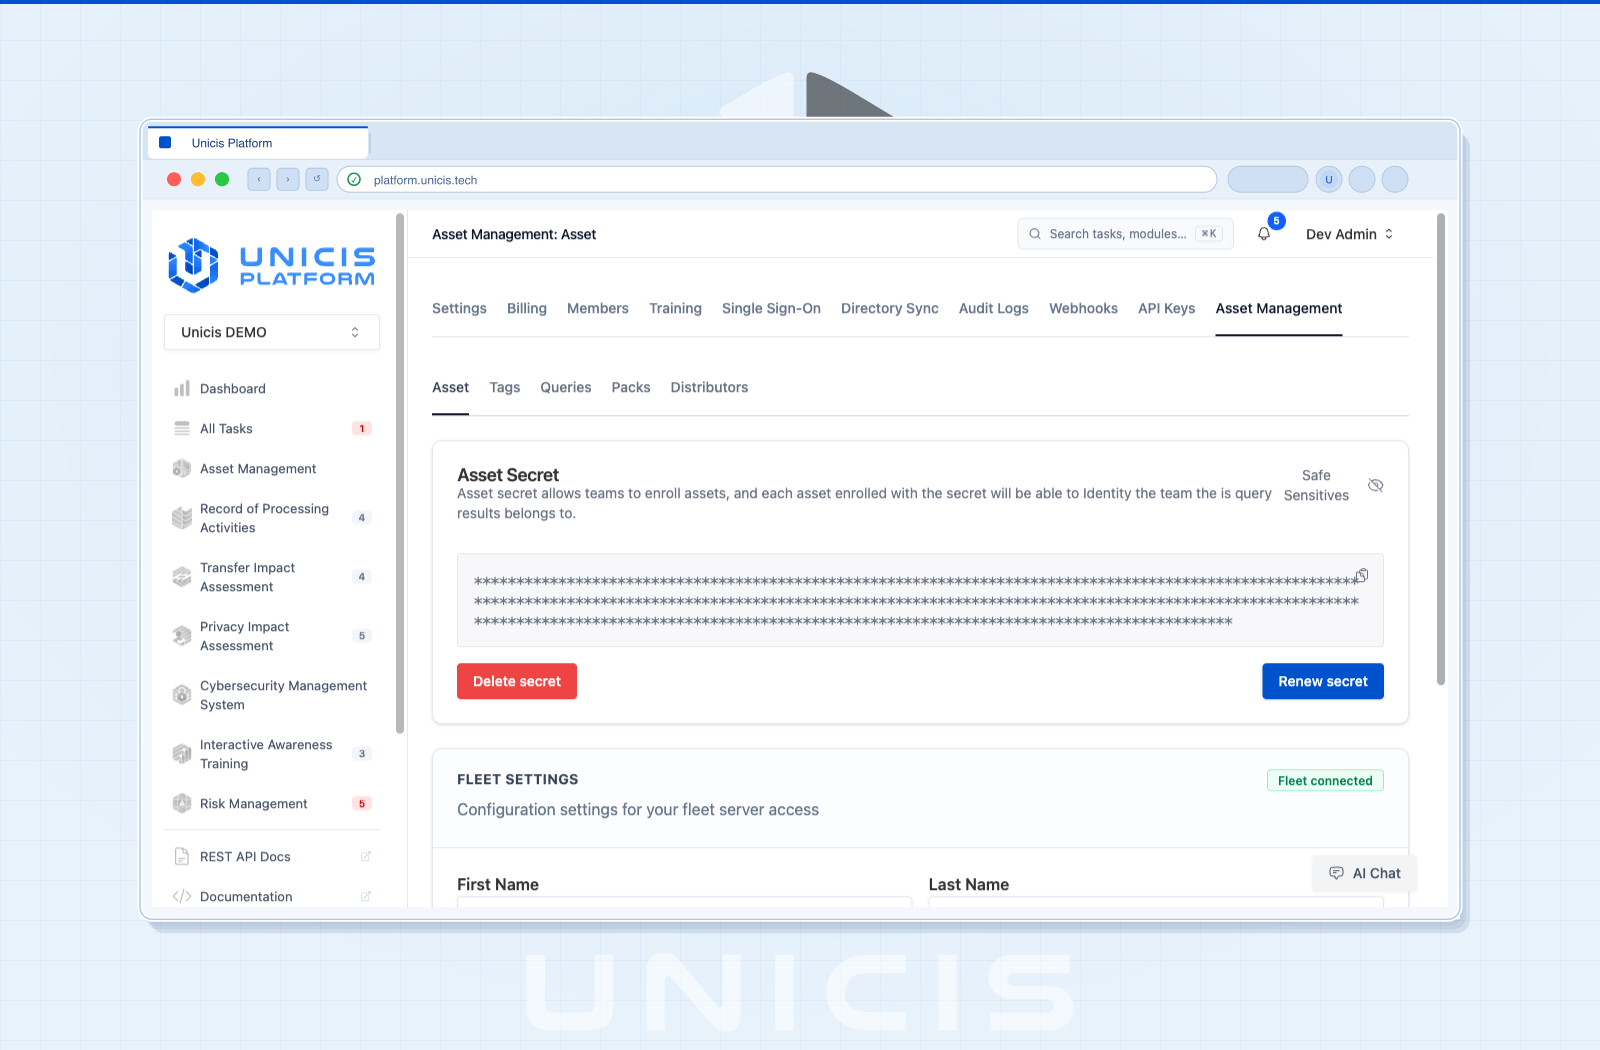
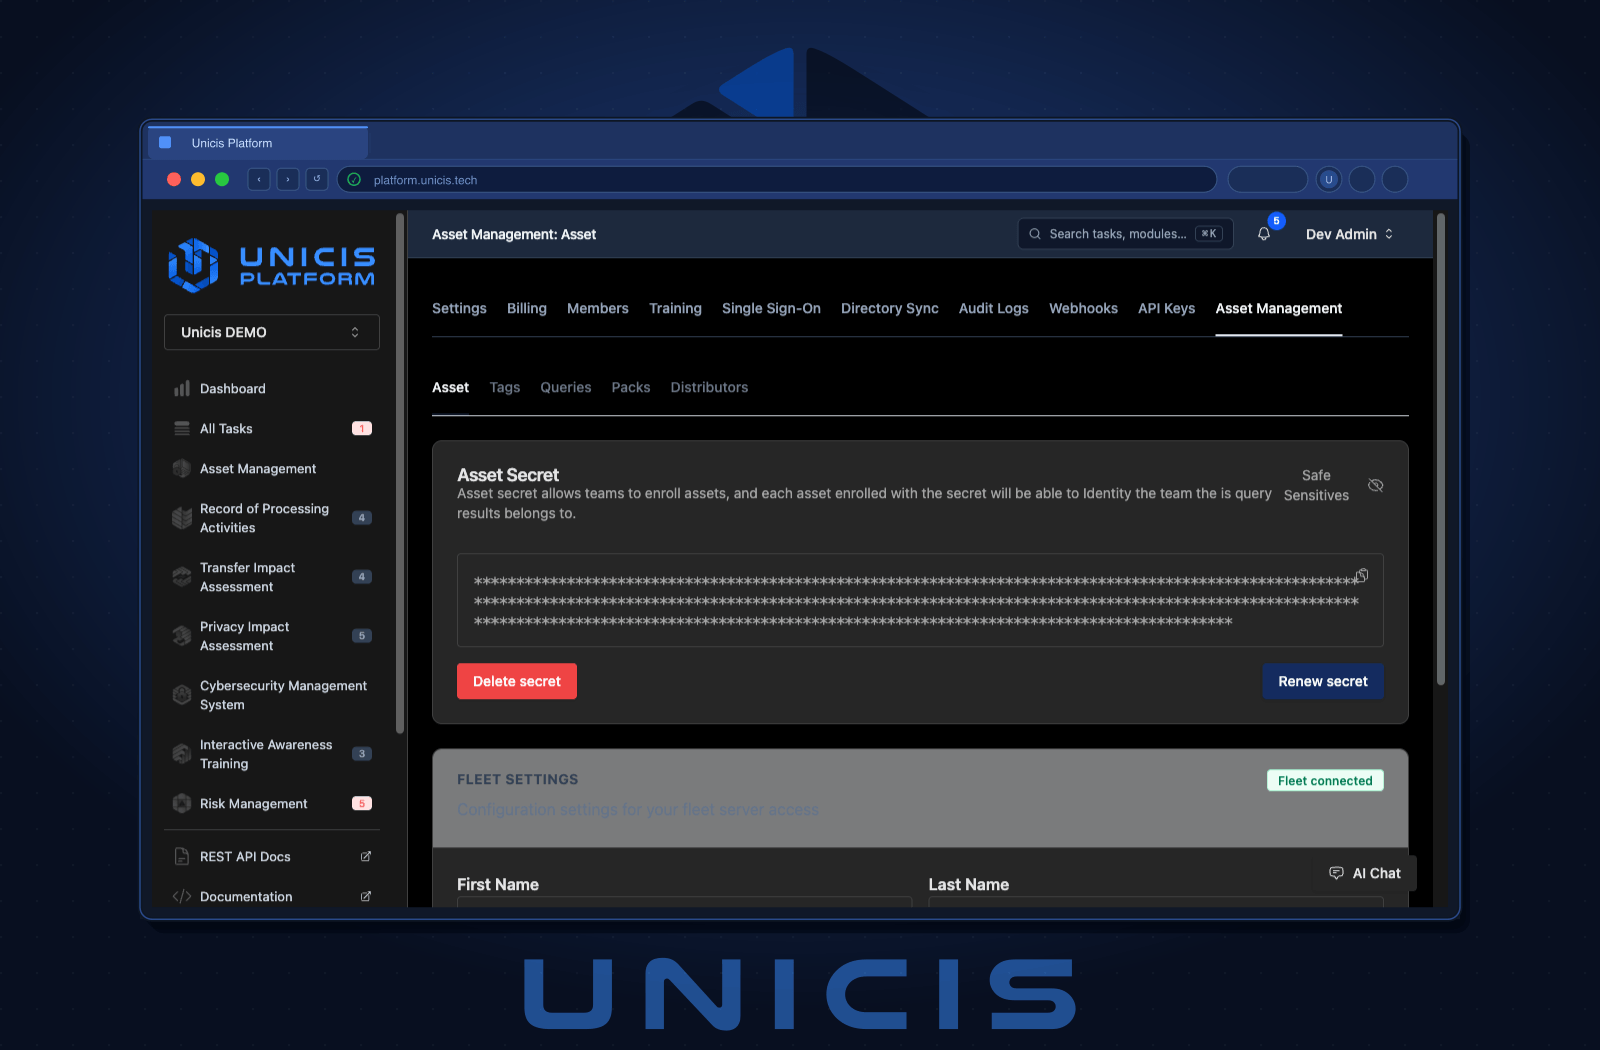
Every team gets its own Fleet tenant, its own enrollment secret, and its own TLS material. Management calls are scoped by team ID at the API layer, so one team can never read another team’s assets, queries, or results — the property that makes multi-tenant asset monitoring defensible in an audit.
- Per-team enrollment secret, rotatable on demand
- Per-team TLS certificate with agent-side certificate pinning
- Every management endpoint scoped by team ID
- Separate Fleet credential per user — platform login is not fleet login
- Fleet roles mapped from platform roles on every connection
Evidence That Lands in Your Compliance Program
An asset inventory is not a side project — it is a named control in every framework Unicis supports. This module lives inside the same platform as your controls, risks, and tasks, so the inventory you build for ISO 27001 A.5.9 is the same one your NIS2 and CIS Control 1 evidence points at.
- ISO/IEC 27001:2022 A.5.9 — Inventory of information and other associated assets
- CIS Controls v8.1 — Control 1 (Enterprise Assets) and Control 2 (Software Assets)
- NIST CSF 2.0 — ID.AM Asset Management
- NIS2 and SOC 2 asset management expectations
- Asset task analysis links enrolled assets to platform tasks
Five Steps From Zero to Live Inventory
No agent server to run, no certificates to hand-roll, and a clean exit when you are done.
Bootstrap
An admin creates the team Fleet account and generates the enrollment secret.
Enroll
Teammates get a 24-hour invitation with a temporary password they must replace on first login.
Install
Copy the generated osquery install and enrollment command for each platform.
Monitor
Assets check in, packs run on schedule, and live queries answer questions on demand.
Retire
Disconnect Fleet and the team’s data is deleted after your configured retention window.
Built for Teams With Auditors in the Room
Granular roles, a separate Fleet credential per user, and a deletion path you control.
Role-based access
Six dedicated permissions cover the dashboard, connection, assets, queries, packs, and tags. Owners and admins hold everything; auditors get a read-only view of the inventory and analysis, and never see the enrollment secret.
Separate Fleet credential
Platform login does not grant fleet access. Users are invited with a 24-hour enrollment token and a temporary password they must replace on first login, and admins can revoke fleet access at any time.
Disconnect and deletion
Disconnecting Fleet expires access immediately and schedules the team's fleet data for deletion after your configured retention window. Reconnect before it elapses and nothing is lost.
Available on Ultimate
Asset Inventory Management ships with the Ultimate plan, on Unicis Cloud or self-hosted.
Ultimate
Everything in Premium, plus the full asset inventory stack.
- Unlimited asset enrollment
- Windows, macOS, and Linux (deb & rpm) agents
- Saved queries, packs, and tags
- Distributed (live) queries with result tracking
- Per-asset status logs, result logs, and configuration view
- Per-team enrollment secret and TLS material
- Self-hosted Unicis Fleet deployment, from a private GitLab repository
Know what you actually run
Discover, enroll, and continuously monitor every endpoint — with evidence your auditors can verify.